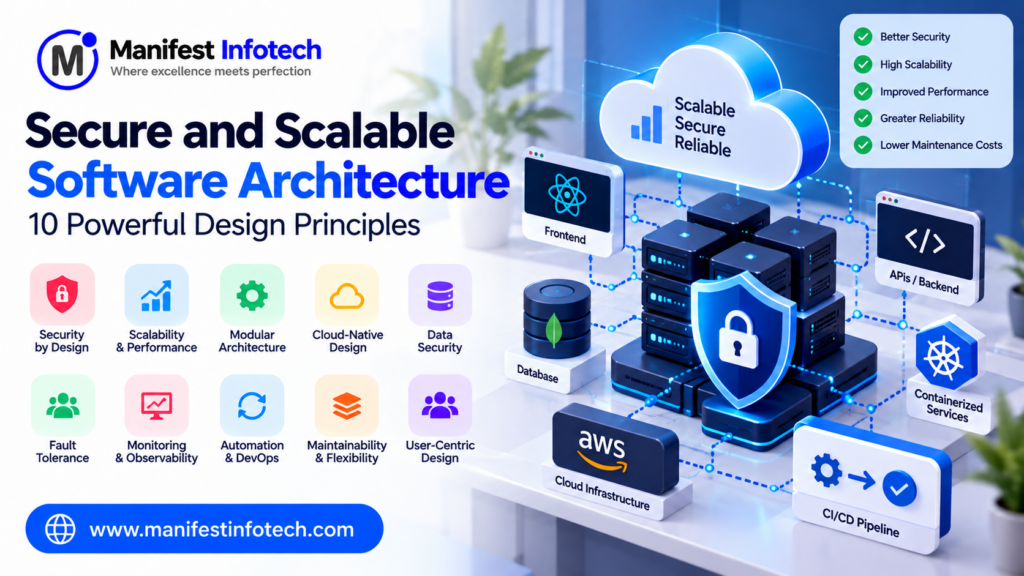
Secure and Scalable Software Architecture: 10 Powerful Design Principles
Modern software applications must do more than simply work. They need to protect sensitive information, support increasing numbers of users, remain available during unexpected failures, and adapt as business requirements change. This is why designing a Secure and Scalable Software Architecture is essential for startups, growing businesses, and enterprise software projects.
A poorly designed application may perform well during its first few months but struggle when traffic increases. It may also expose customer information, become difficult to maintain, or require expensive changes as the business grows.
A well-planned architecture addresses these challenges from the beginning. It combines security, performance, reliability, maintainability, and flexibility to create a strong foundation for long-term software development.
In this guide, we will explain how to design a secure and scalable software architecture, explore important architectural patterns, discuss practical technologies, and share ten principles that development teams can apply to real-world projects.
What Is Software Architecture?
Software architecture is the high-level structure of an application. It defines how different components communicate, how information is stored and processed, how users access the system, and how the application is deployed and maintained.
It includes decisions about:
- Frontend and backend technologies
- Application modules and services
- Database structure and data ownership
- APIs and communication methods
- Authentication and authorization
- Cloud infrastructure and deployment
- Monitoring, backups, and disaster recovery
For example, an online shopping platform may contain a customer-facing website, an API layer, product and order services, a payment integration, a database, and a notification service.
The architecture defines how these components work together and how they remain secure and responsive as the number of customers increases.
Why Do Security and Scalability Matter?
Security and scalability are connected to the long-term success of a software product.
1. Protect sensitive information
Applications often store customer details, payment-related information, business records, and login credentials. Security controls help prevent unauthorized access, data leaks, and misuse.
2. Support business growth
As a product becomes popular, the number of users, requests, and stored records may increase. A scalable architecture helps the system handle this growth without requiring a complete redesign.
3. Improve application availability
A reliable system should continue operating when an individual service, server, or external dependency experiences a problem.
4. Reduce maintenance costs
Clear service boundaries, reusable components, automated testing, and consistent deployment processes make applications easier to maintain.
5. Build customer trust
Users are more likely to trust applications that protect their information, respond reliably, and handle errors safely.
10 Powerful Principles for Designing a Secure and Scalable Software Architecture
1. Start with Clear Business and Technical Requirements
Before selecting a technology stack, understand what the application needs to achieve.
Identify the functional requirements, such as registration, login, payments, reporting, search, and notifications. Then define non-functional requirements, including:
- Expected number of users
- Peak requests per second
- Response-time expectations
- Availability requirements
- Data storage and retention needs
- Security and compliance requirements
- Recovery time and acceptable data loss
- Expected growth over the next few years
For example, an internal employee management application may have a few hundred users, while a public e-commerce platform may experience thousands of simultaneous requests during a sale.
These applications should not automatically use the same architecture.
Practical tip: Define measurable performance and reliability targets before development. Avoid vague requirements such as “the application should be fast.”
2. Choose the Right Architectural Pattern
The architectural pattern determines how application components are organized.
Common options include:
Monolithic architecture
A monolithic application keeps most business functionality within one deployable application.
Benefits:
- Simple to develop and deploy initially
- Easier to debug in smaller projects
- Lower infrastructure complexity
- Suitable for many early-stage products
Limitations:
- The application can become difficult to maintain as it grows
- Components may become tightly coupled
- Scaling individual features independently is difficult
Microservices architecture
Microservices divide an application into smaller, independently deployable services. Each service handles a defined business responsibility.
Benefits:
- Independent deployment and scaling
- Clearer ownership of business functionality
- Different services can use suitable technologies
- Failures can be isolated when boundaries are designed correctly
Limitations:
- More infrastructure and operational complexity
- Network communication introduces latency and failure possibilities
- Monitoring, security, and data consistency become more challenging
Modular monolith
A modular monolith keeps one deployable application but separates business areas into well-defined modules.
It can provide a useful balance for many growing products: clear internal boundaries without the operational overhead of multiple distributed services.
Which pattern should you choose?
Start with a modular monolith when the product is relatively small and the team wants to move quickly. Consider microservices when independent deployment, separate scaling requirements, team ownership, or domain boundaries justify the additional complexity.
Do not adopt microservices simply because they are popular.
3. Implement Security from the Beginning
Security should be part of architecture and development planning, not something added just before launch.
Important security practices include:
- Use HTTPS with modern TLS configurations.
- Store passwords using a suitable password-hashing algorithm such as Argon2id or bcrypt.
- Implement secure authentication and authorization.
- Apply role-based access control where appropriate.
- Validate and sanitize untrusted input.
- Protect APIs against unauthorized access and abuse.
- Store secrets outside source code.
- Keep dependencies and infrastructure updated.
- Record important security events without logging sensitive data.
Authentication verifies who a user is. Authorization determines what that user is allowed to do. Both are necessary.
For example, a customer should not be able to access an administrator’s dashboard simply by changing a URL or modifying a request.
Use the principle of least privilege: users, services, and deployment processes should receive only the permissions they need.
4. Design APIs with Strong Security and Versioning
APIs allow the frontend, backend, mobile applications, and external services to communicate.
A well-designed API should have consistent naming, clear request and response formats, documented error handling, and appropriate access controls.
Recommended practices:
- Use REST or GraphQL according to the application’s requirements.
- Validate request parameters and payloads on the server.
- Apply authentication and authorization to protected endpoints.
- Use rate limiting to control excessive requests.
- Set request size limits and sensible timeouts.
- Avoid exposing internal stack traces or sensitive information.
- Version APIs when changes could break existing consumers.
- Document API contracts using OpenAPI where appropriate.
For example:
GET /api/v1/products
POST /api/v1/orders
GET /api/v1/orders/{orderId}
The backend must verify that the authenticated user is allowed to view the requested order. Knowing or guessing an order ID must not be sufficient to access another customer’s data.
5. Select a Database Strategy That Supports Growth
Database design has a major impact on application security and scalability.
Common database options include:
Relational databases
PostgreSQL and MySQL are suitable for structured data, relationships, transactions, and applications that require strong consistency.
NoSQL databases
MongoDB and other document databases can be useful when the data model is document-oriented and flexible schemas are valuable.
The correct choice depends on query patterns, relationships, consistency requirements, transaction needs, and operational experience.
Useful database practices include:
- Design indexes around real query patterns.
- Use parameterized queries or safe database libraries.
- Apply database access permissions carefully.
- Encrypt sensitive information where appropriate.
- Back up data regularly and test restoration.
- Monitor slow queries and connection usage.
- Use connection pooling.
- Plan data retention and deletion policies.
For larger applications, read replicas, partitioning, or sharding may help address specific workload bottlenecks. These techniques should be introduced based on measured needs rather than assumptions.
6. Build for Horizontal Scalability
Scalability is the ability of a system to handle increasing demand while maintaining acceptable performance.
There are two common approaches:
Vertical scaling: Increase the CPU, memory, or storage capacity of an existing server.
Horizontal scaling: Add more application instances or servers to distribute workloads.
Horizontal scaling is often useful for applications with growing or unpredictable traffic.
To support it:
- Keep application instances as stateless as practical.
- Store shared session state in a suitable shared store.
- Put a load balancer in front of application instances.
- Use queues for background processing.
- Avoid relying on local server files for shared application data.
- Configure autoscaling using meaningful metrics.
- Test how the application behaves when instances are added or removed.
For example, a platform may run multiple backend instances behind a load balancer. When traffic increases, additional instances can be started, provided the database and other dependencies can also handle the increased load.
7. Use Caching and Asynchronous Processing
Not every request needs to be processed from the database or completed during the user’s active request.
Caching stores frequently requested information so that it can be served faster.
Possible caching layers include:
- Browser caching for suitable static resources
- CDN caching for public assets
- Application caching with Redis
- Database query caching where supported and appropriate
Caching must include a plan for expiration, invalidation, and data freshness. Avoid caching private or user-specific information in shared caches without correct isolation.
Asynchronous processing moves time-consuming tasks outside the immediate user request.
Examples include:
- Sending emails
- Generating reports
- Processing uploaded files
- Sending notifications
- Running scheduled jobs
A message broker or job queue can help distribute these tasks to background workers.
Design queue consumers to handle duplicate delivery safely. Use retries with backoff, dead-letter queues, and monitoring so that failed jobs do not disappear unnoticed.
8. Design for Reliability and Failure Recovery
No application can depend on every server, database, network connection, or external service working perfectly all the time.
A reliable architecture anticipates failure.
Use these techniques:
- Timeouts: Prevent requests from waiting indefinitely.
- **Retries with backof
OWASP Secure by Design Framework — architecture-level security principles, trust boundaries, access controls, and resilience.
OWASP Secure Cloud Architecture Cheat Sheet — cloud security and threat modeling.
NIST Secure Software Development Framework (SSDF) — integrating security into the software development lifecycle.
Microsoft Azure Architecture Best Practices — reliability, caching, data partitioning, and scalable application design.
AWS Well-Architected Framework — security, reliability, performance, cost optimization, and operational excellence.